De-risk detection so you can focus on the most critical incidents, changes, and malicious events first.
including PCI DSS 4.0, NERC CIP, FISMA, SOX, NIST, HIPAA, CIS controls, GDPR
to focus on what matters most
and improve PCI compliance almost instantly
Track changes to files, folders and registry objects in real time
Continuously monitor critical assets for changes across diverse cloud and on-premises environments of all sizes, including large global enterprises.
Prioritize alerts and reduce noise with threat intelligence from Trusted Sources and File Reputation context.
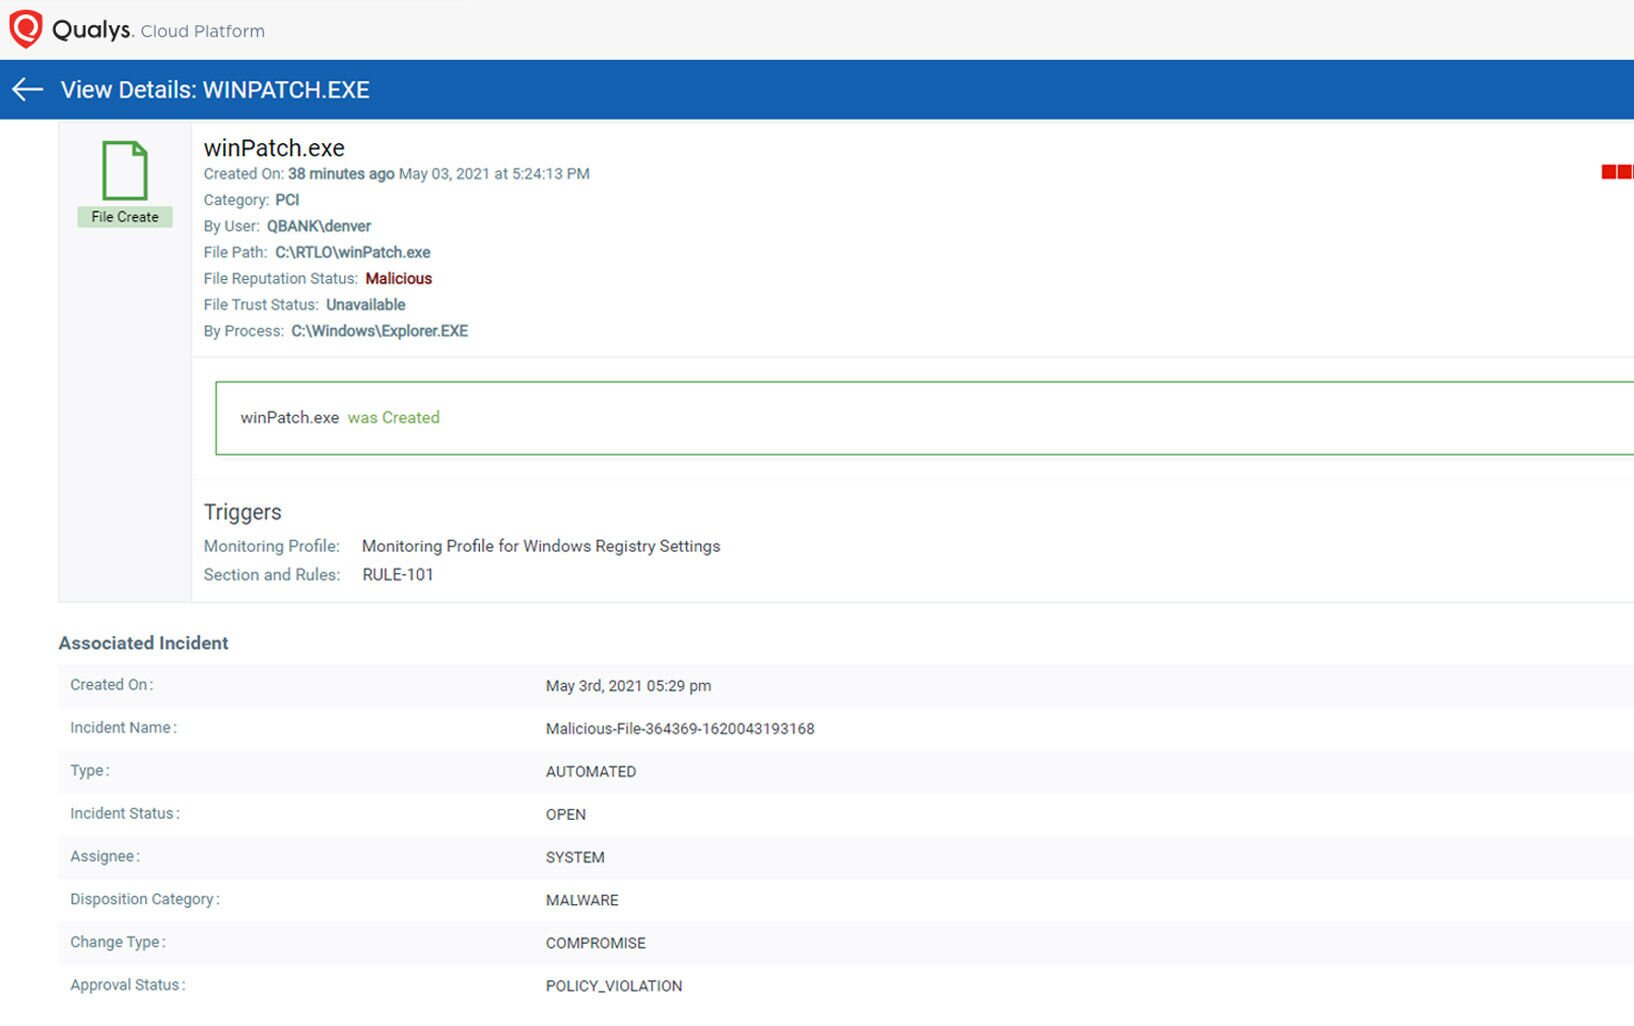
Quickly identify malicious or suspicious changes to focus on critical risks.
Includes FAM and Agentless Network Support
Meet FIM compliance for PCI DSS 4.0 and more
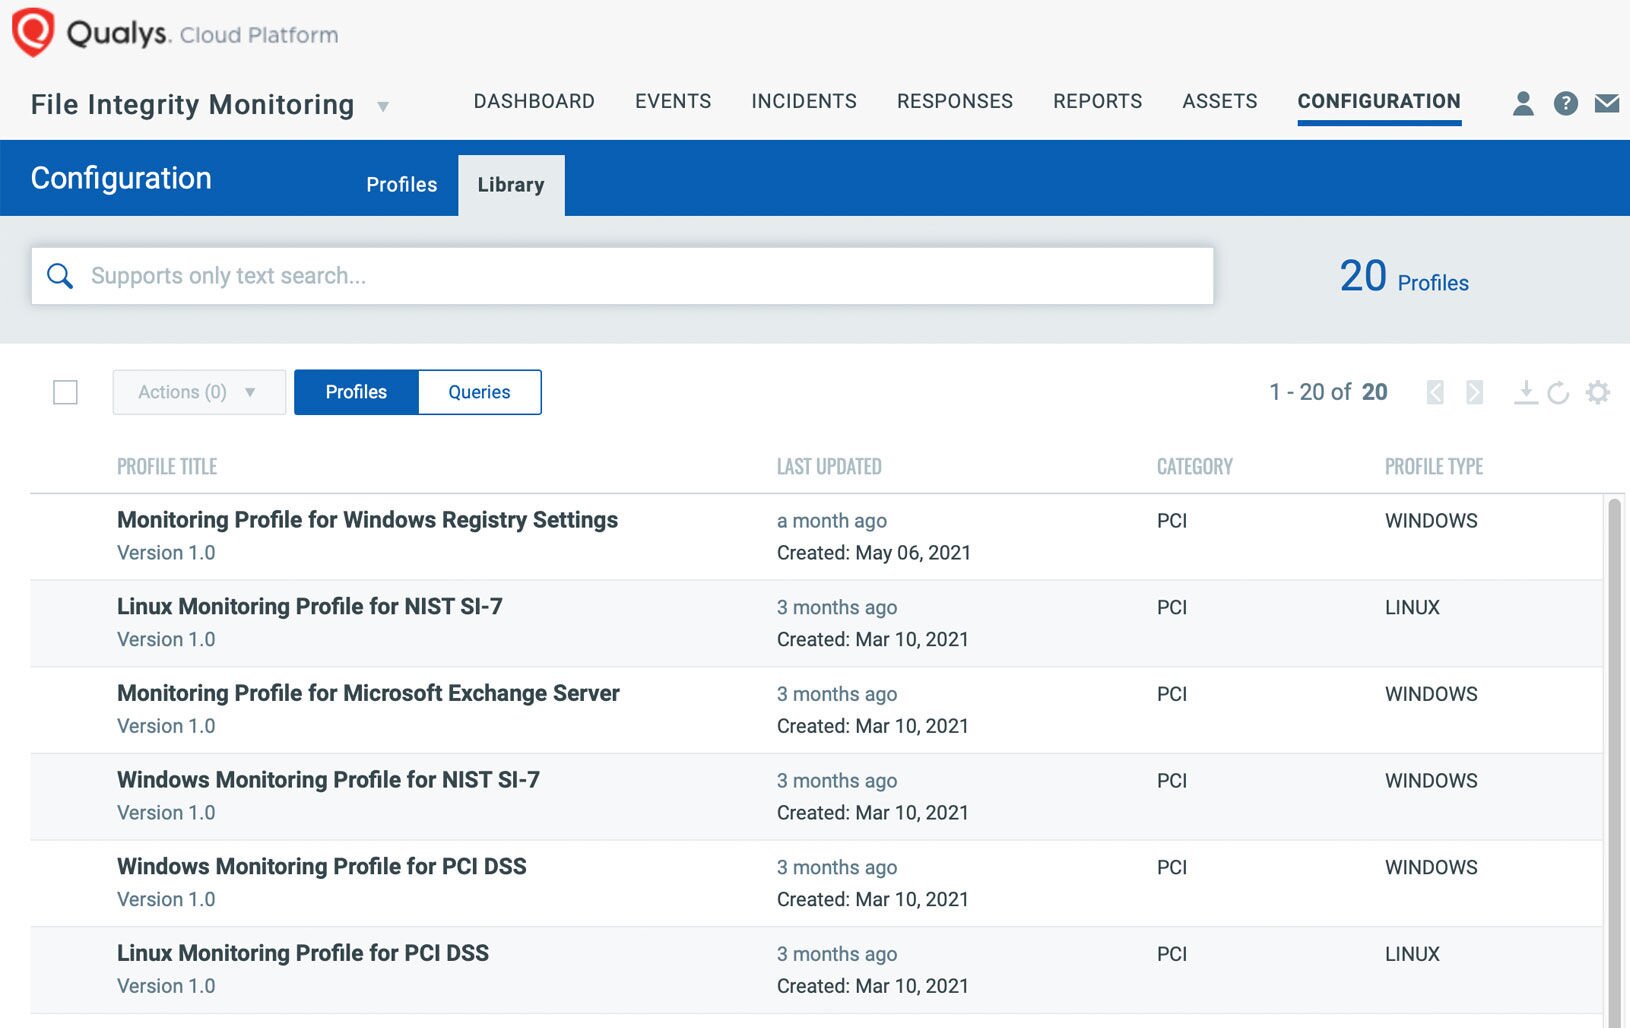
With one click, I can leverage my Qualys Agent to quickly activate file monitoring. Asset tags ensure new assets are discovered and configured for FIM, and out-of-the-box profiles get me up and running quickly, further reducing onboarding time and helping ensure we are fully prepared for PCI DSS 4.0 compliance.
Self-updating and self-healing to reduce maintenance for uninterrupted monitoring and limited impact on endpoints.
Gain visibility of malicious, unauthorized, and anomalous activities including who made changes with automated event correlation and alerts that streamline incident management.
Leverage existing monitoring profiles and well-defined alert management rules to ensure compliance with PCI DSS 4.0 Sections 10.5.5 and 11.5.
Reduce false positive FIM alerts and add context with automatic identification of malicious changes while whitelisting trusted changes.
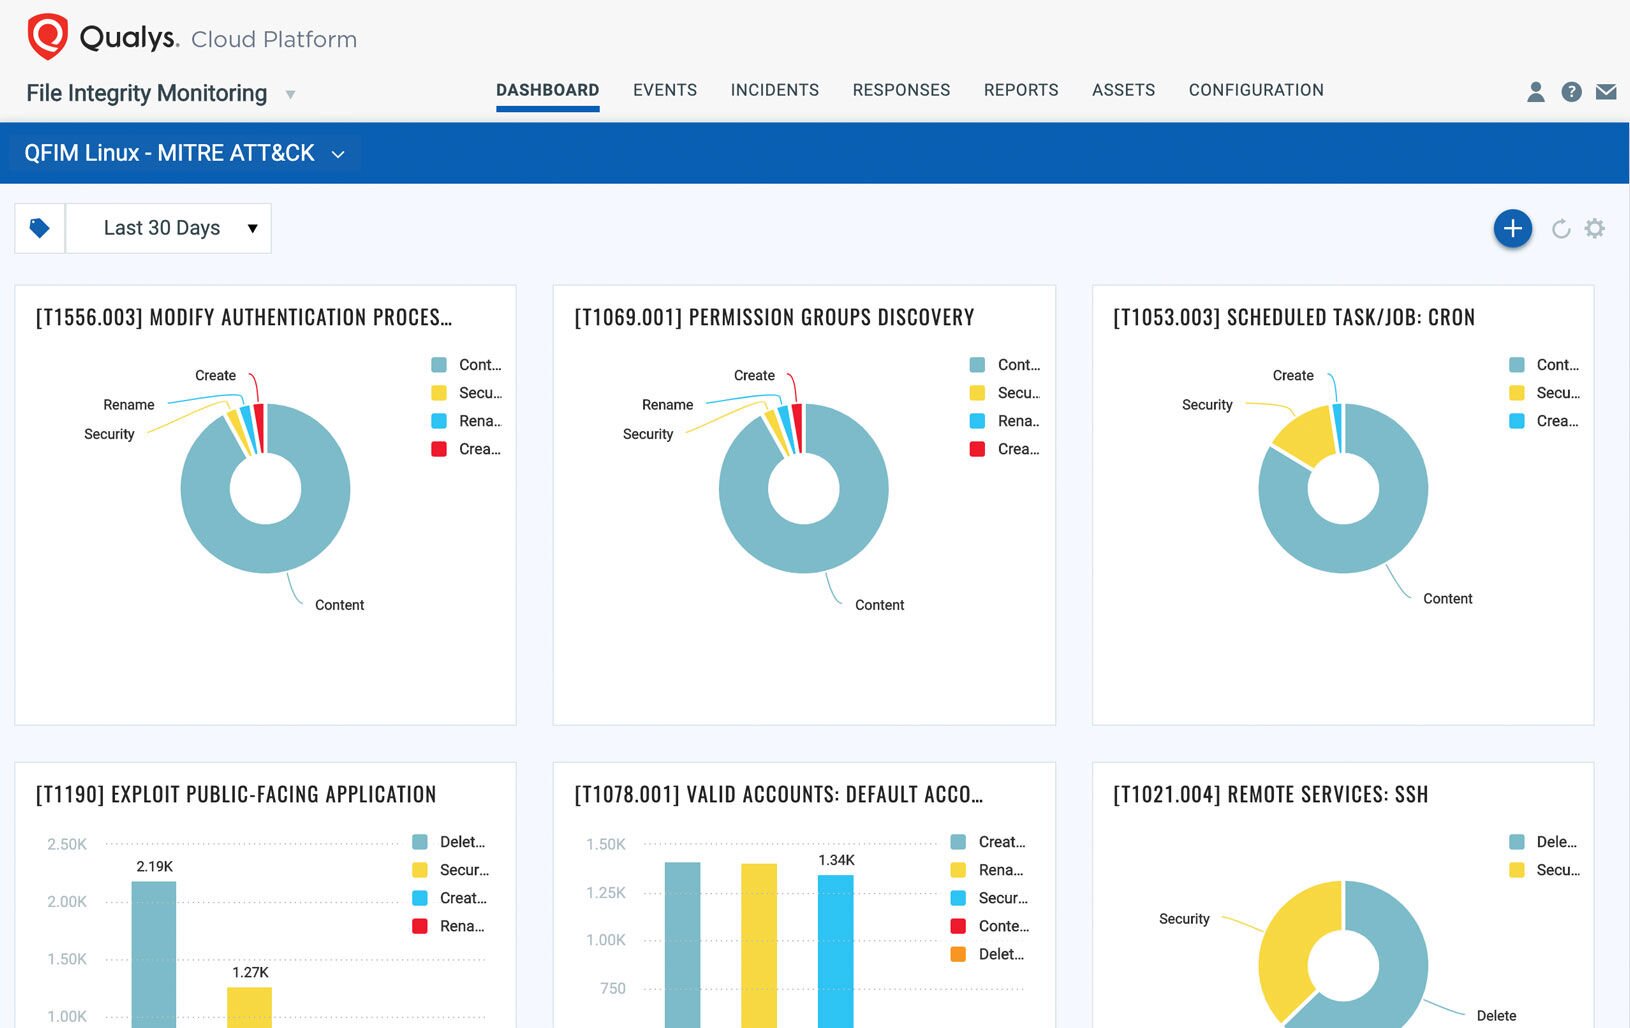
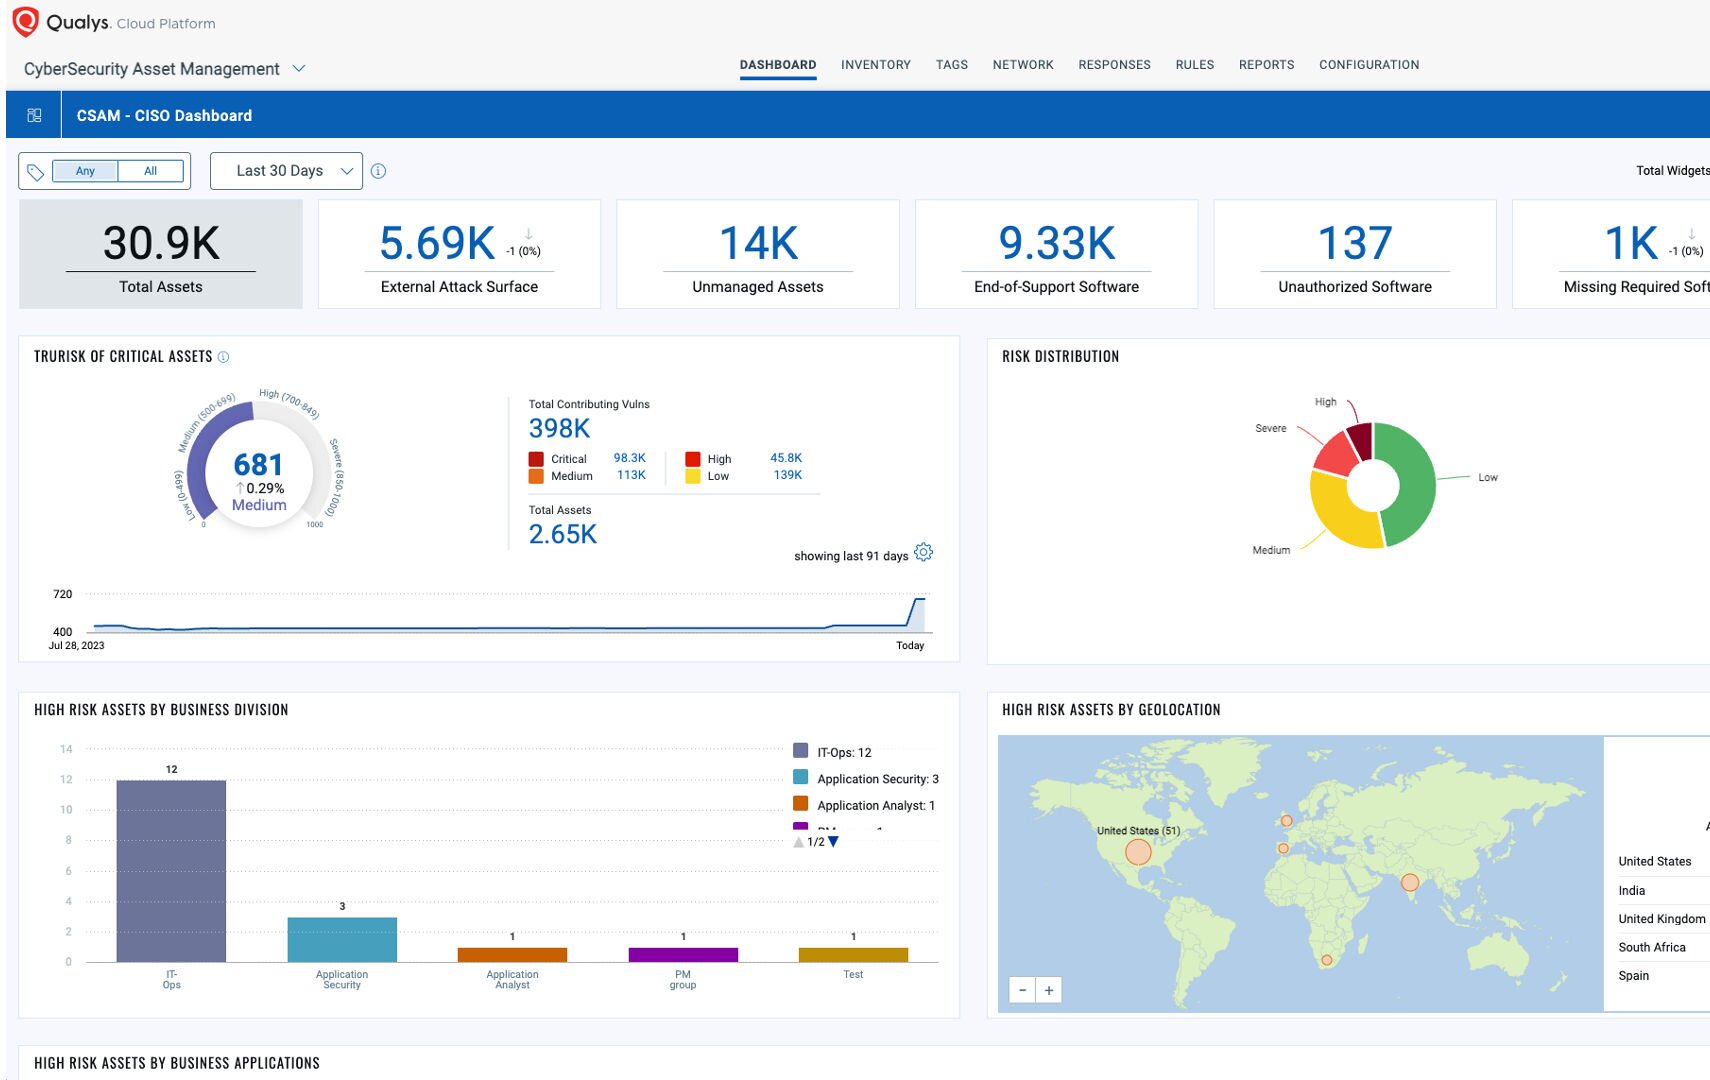
Integrates with the Enterprise TruRisk® Platform to leverage dynamic dashboards and widgets and initiate one-click workflows to remediate risks associated with alerts.
Create rules for real-time alerts and incidents to quickly identify and respond to unauthorized activity.
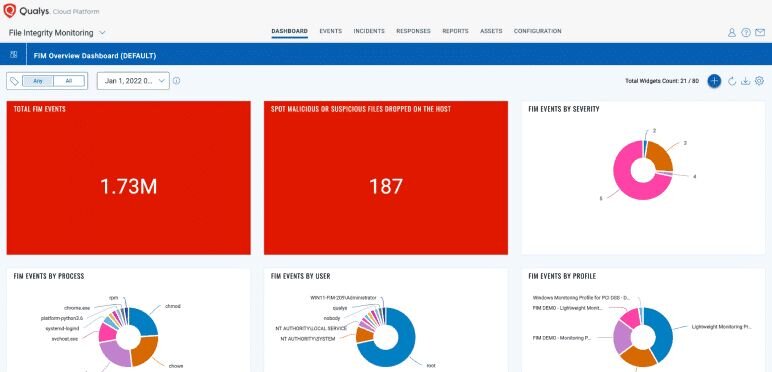
Organizations handling credit cards must comply with PCI DSS 4.0 by implementing FIM.
Verizon's Payment Security Report reveals that 9.8% of organizations fail audits due to lacking File Integrity Monitoring (FIM).
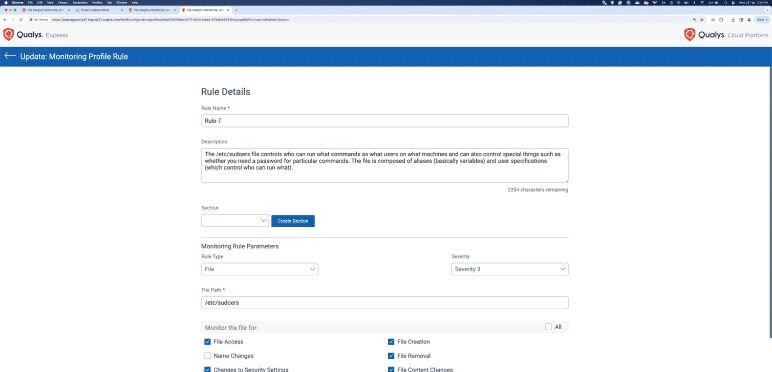
Security practice that involves tracking and logging access to sensitive files.
Compliance regulations such as GDPR, CCPA, SOX, HIPAA mandate monitoring of sensitive data access by organisations.
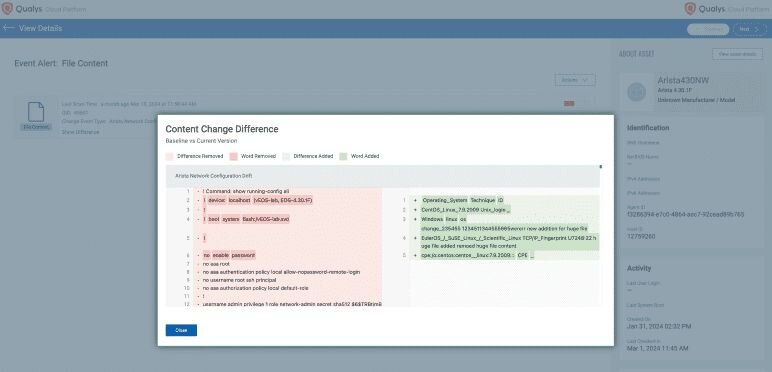
When a network device's configuration changes, logging the modification and timestamp is crucial.
Lacking measures to detect changes in network configurations can result in compliance failures with regulatory standards.

FIM is a security process that detects and alerts on unauthorized changes to critical system files, directories, and registry settings in real time. It is essential for detecting malicious activity and meeting compliance mandates like PCI DSS.
Yes. FIM is a mandatory requirement for many regulations, including PCI DSS 4.0.1, HIPAA, FISMA, SOX, and NIST. Qualys FIM provides pre-configured profiles to help you meet the specific requirements of these standards out of the box.
Yes. By monitoring for unauthorized access and changes to critical files (File Access Monitoring), FIM can detect anomalous activity indicative of an insider threat, such as an employee accessing or modifying sensitive data outside of their normal duties.
Yes. Qualys FIM offers robust integration with leading SIEM and SOAR platforms, including IBM QRadar, LogRhythm, and Cortex XSOAR. This allows you to forward high-fidelity FIM alerts to your central security operations hub for correlation and response.
FIM is a key component of a ransomware defense strategy. It can detect the initial file modifications and creations characteristic of a ransomware attack in real time, providing an early warning that allows for rapid response to isolate affected systems.
Qualys FIM reduces alert noise by up to 90% using threat intelligence and file reputation data to distinguish malicious changes from benign ones. It also allows whitelisting of trusted processes, ensuring your team focuses only on critical events.
Organizations in regulated industries (finance, healthcare, government) must use FIM for compliance. Any organization looking to enhance its security posture by detecting unauthorized changes and potential breaches in real time will also benefit significantly.