Inside the Qualys Cloud Security Forecast 2026 - Your cloud is working as designed. So is the risk.
Inside the Qualys Cloud Security Forecast 2026 - Your cloud is working as designed. So is the risk.
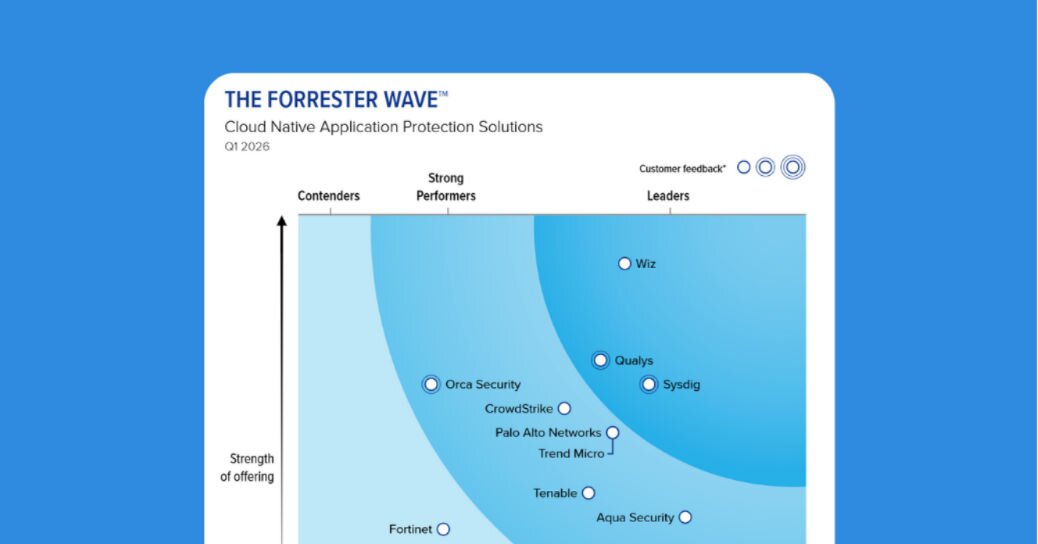
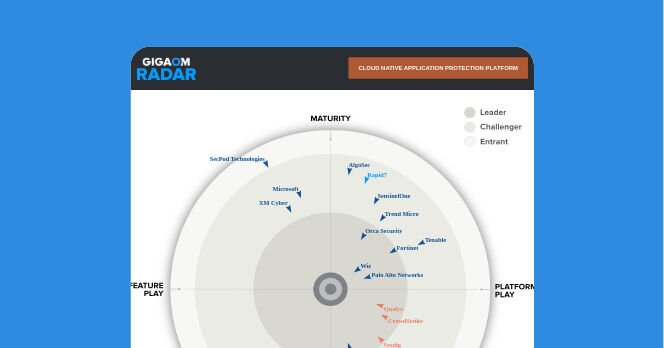
Forrester Wave CNAPP Leader, KuppingerCole 2025 CNAPP Leader and GigaOm Radar Leader and Outperformer. PeerSpot highest rated CNAPP vendor, FedRAMP High Authorization.


Ask AI for a summary of Qualys


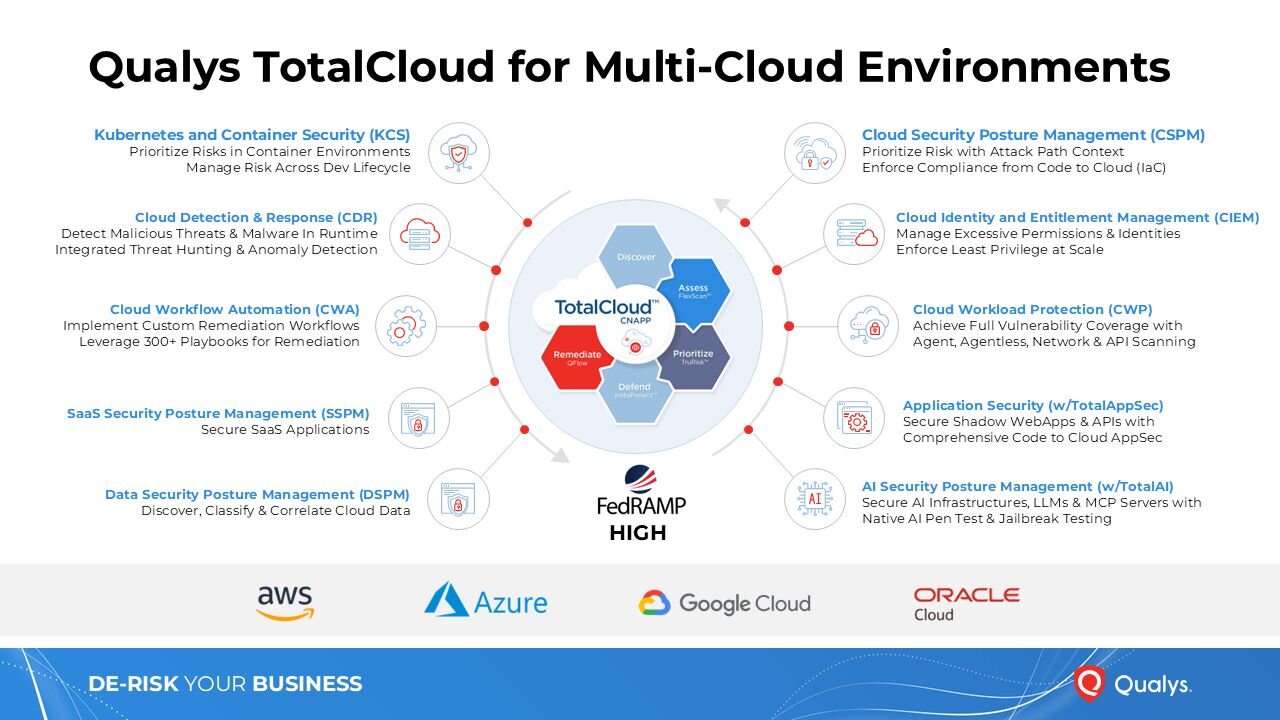
Services to unify cloud visibility and eliminate blind spots from compute to AI
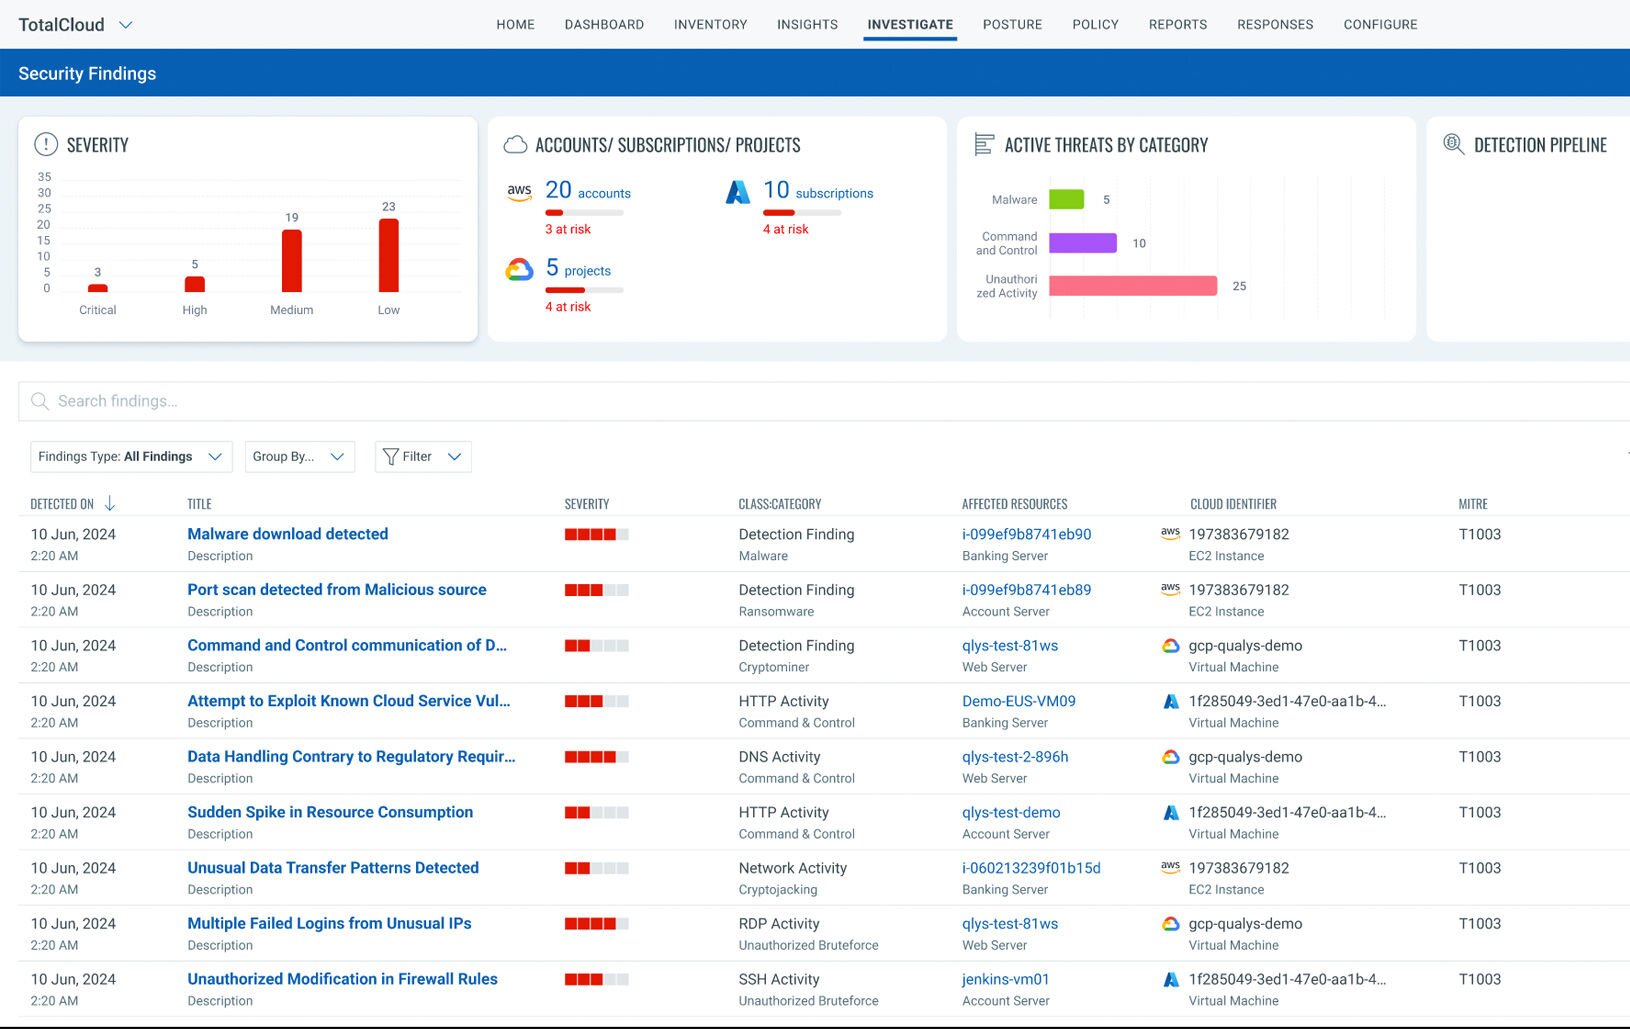
Noise reduction with TruRisk™ for real, exploitable risk visibility versus alert fatigue
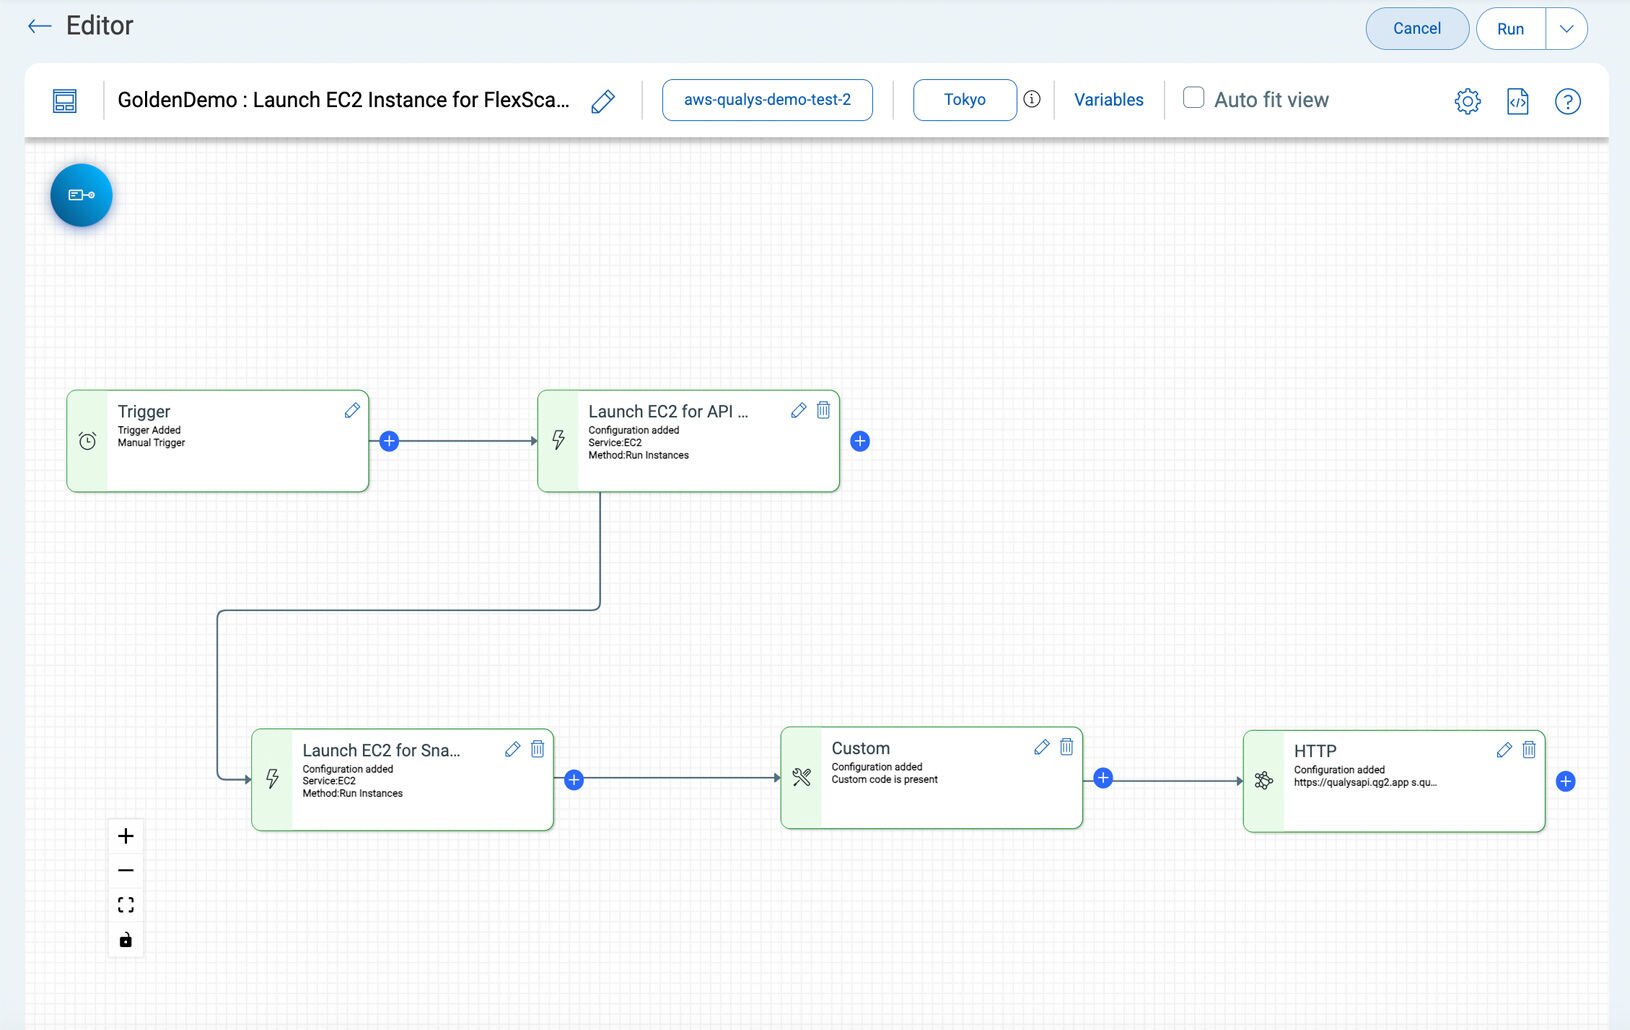
Build and play automated remediation workflows with a no-code orchestration platform.
Automatically discover cloud, container, and SaaS assets across AWS, Azure, GCP, and hybrid environments. Eliminate shadow IT and maintain continuous visibility across your entire attack surface.
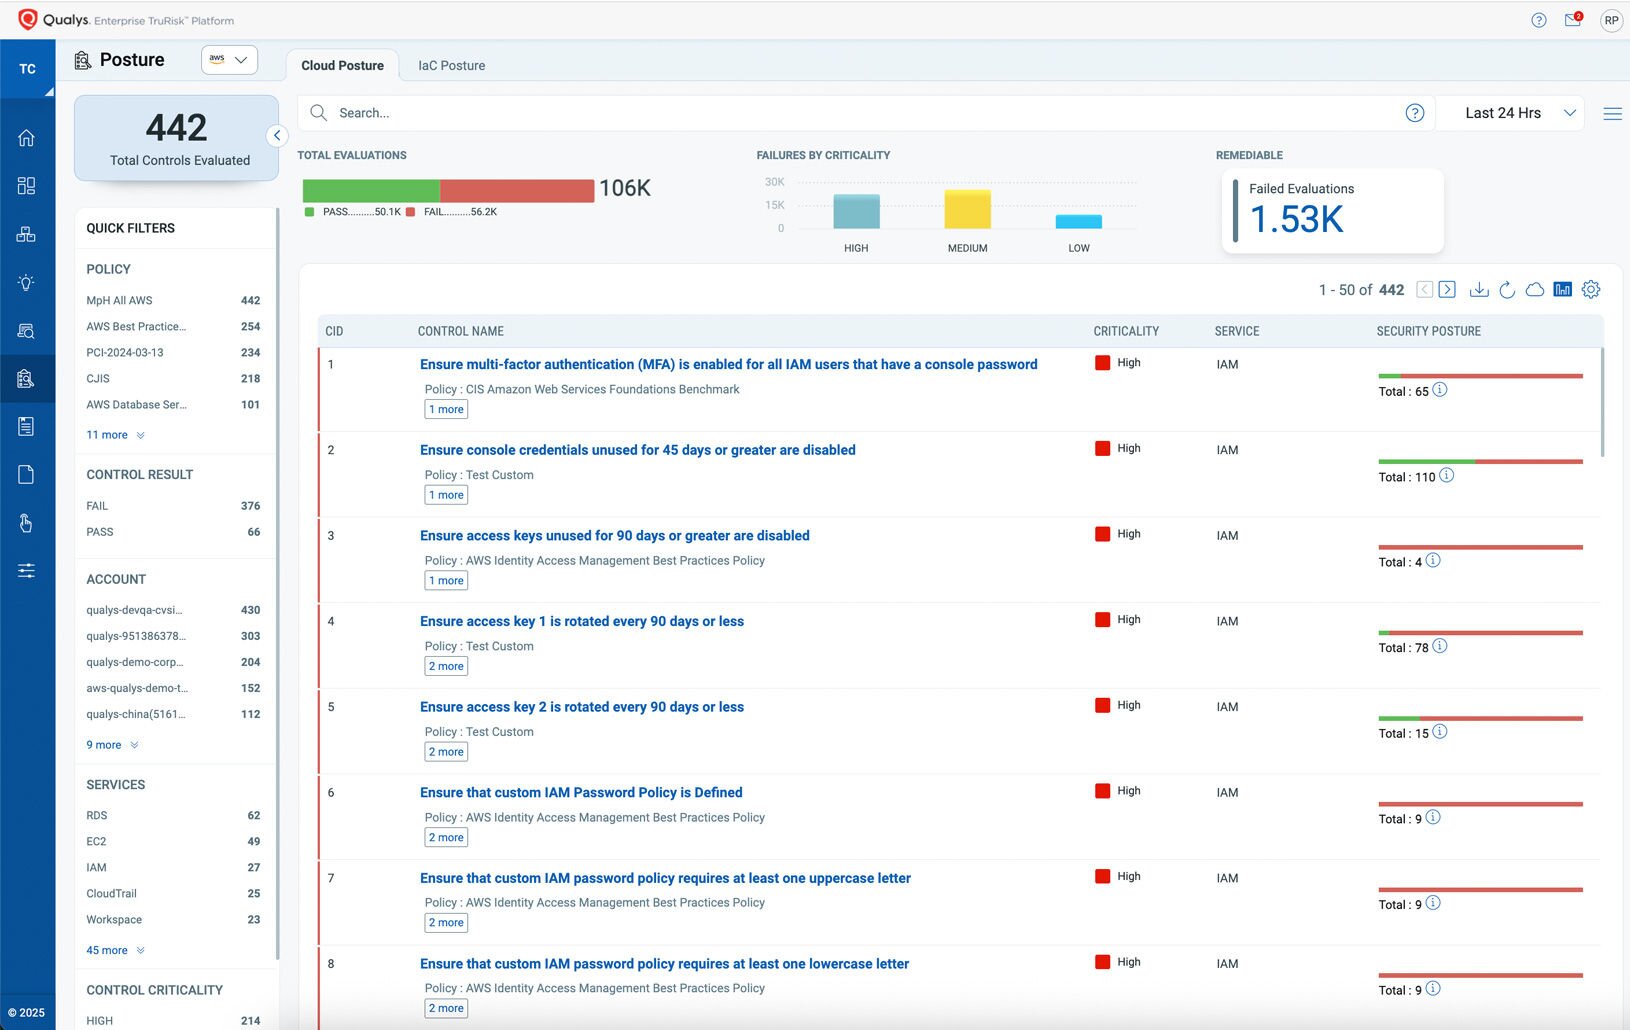
Meet and prove compliance with frameworks across deployed cloud resources and IaC templates such as PCI DSS 4.0, HIPAA 2023, NIST 800-53/171, and GDPR through real-time monitoring, automated policy mapping, and audit-ready dashboards.
Secure The Full Container Lifecycle across Code, Build (CI/CD), Container Registries, and Production Kubernetes Clusters, Hosts and Serverless Workloads In Your Hybrid Cloud. Continuously map and assess image scans to running container posture, attack path, and drift context. Secure Your Kubernetes Control Plane with KSPM to prevent attackers and exploitation with runtime and AI-powered defense. Empower developers to fix left, using runtime-driven context to guide remediation at the source — before risk propagates across the pipeline
Cut through the noise with risk scores based on exploitability, criticality, attack path analysis, and exposure. Focus remediation on exploitable vulnerabilities, not every CVE, and report meaningful risk reduction to the board and stakeholders.
Visualize and enforce least-privilege access across cloud identities, detect toxic permission chains, and automate revocation of risky roles to align with Zero Trust principles. Deepen CIEM + DSPM to correlate identity, permission, and sensitive-data exposure across hybrid infrastructure.
Detect zero-days, fileless malware, and anomalous process behavior with eBPF-based runtime monitoring and machine learning. Instantly contain threats via policy-based QFlow™ response playbooks.
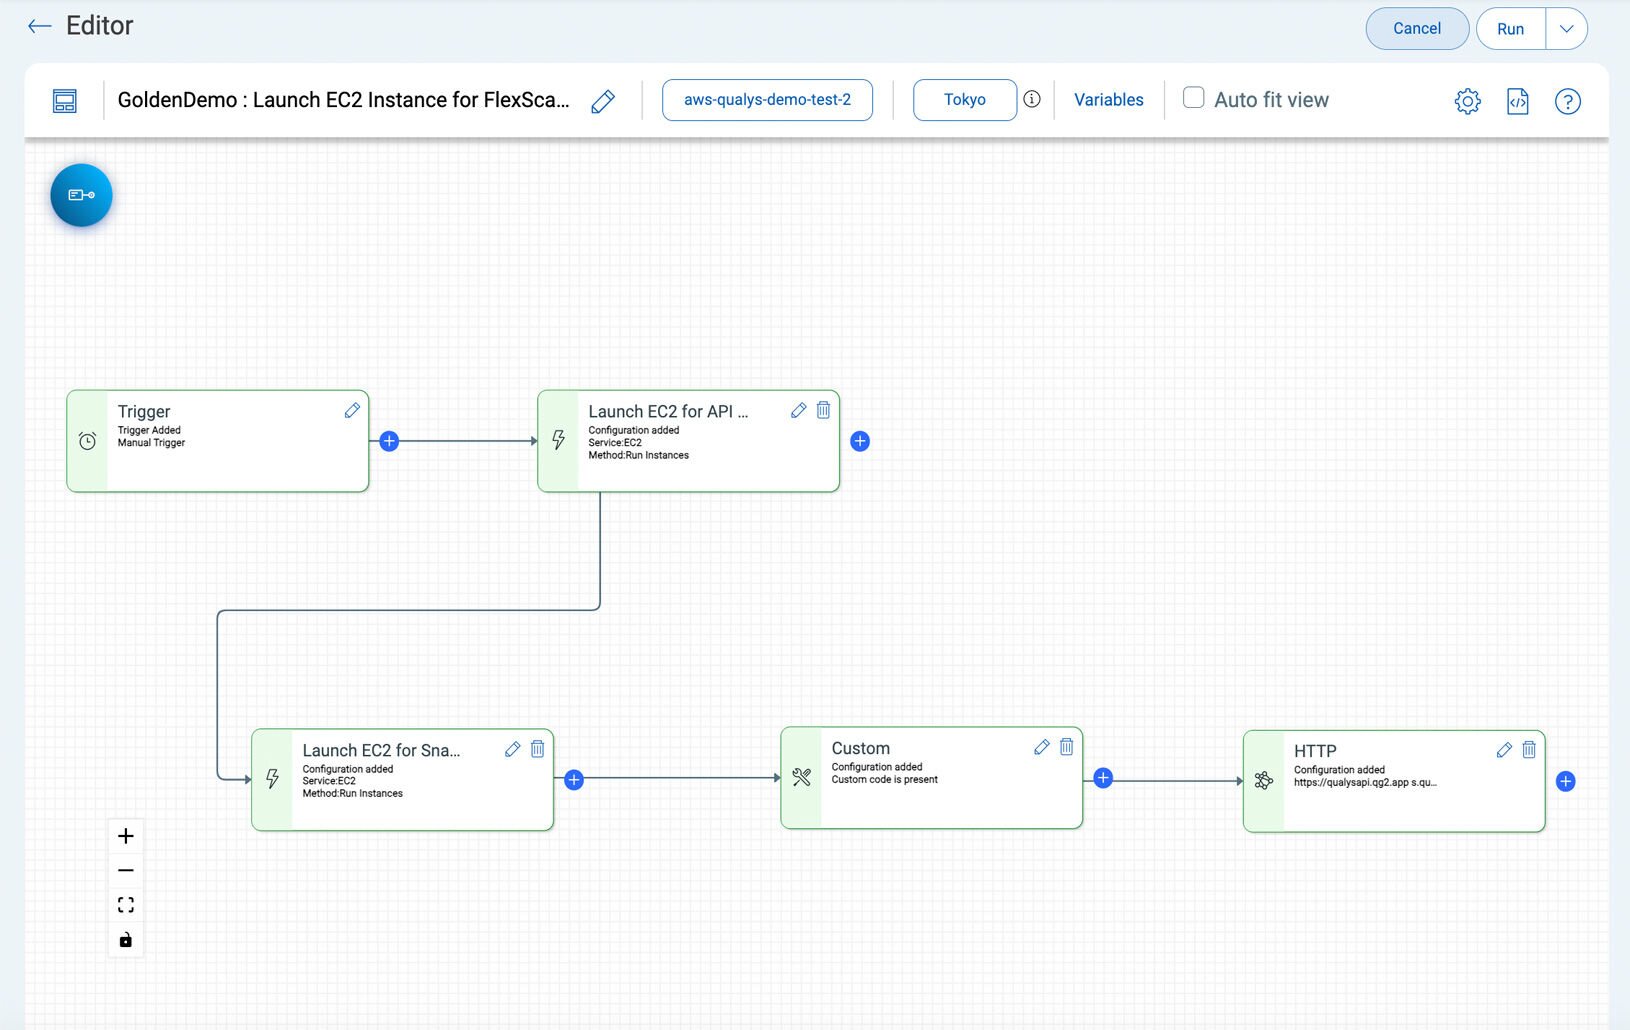
Drag, drop, and deploy custom workflows that remediate vulnerabilities, fix misconfigurations, and trigger ITSM tickets in seconds, no scripts required.
Continuously evaluate 2,000 + resource types across SaaS apps for compliance with 40 + standards, including CIS and ISO 27001, and automate remediation via QFlow™.
Bridge development and security with IaC scanning, API and web app assessment, and attack-path correlation from code to runtime. TotalCloud and TotalAppSec can work together to align Dev and Sec teams and catch vulnerabilities before release.
Gain complete risk visibility into all AI being used in your environment with instant LLM Discovery and Scanning with Total AI across AWS Bedrock, GCP Vertex, Azure Open AI and more.
See your cloud risk the way attackers do.
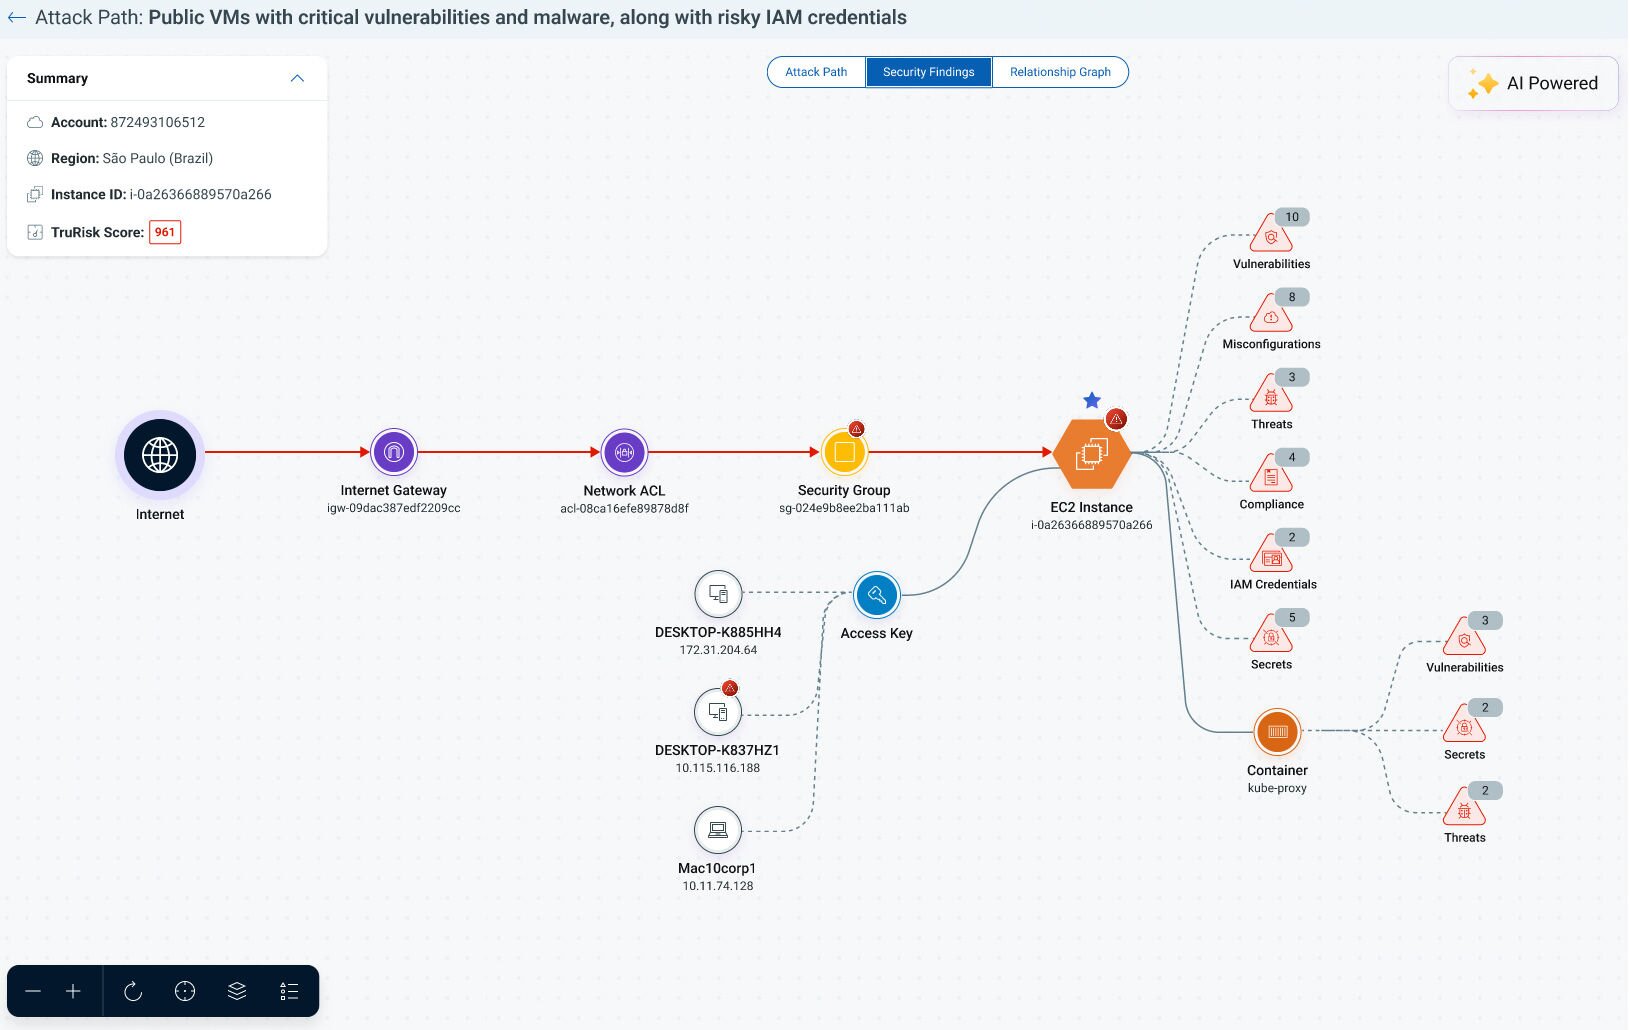
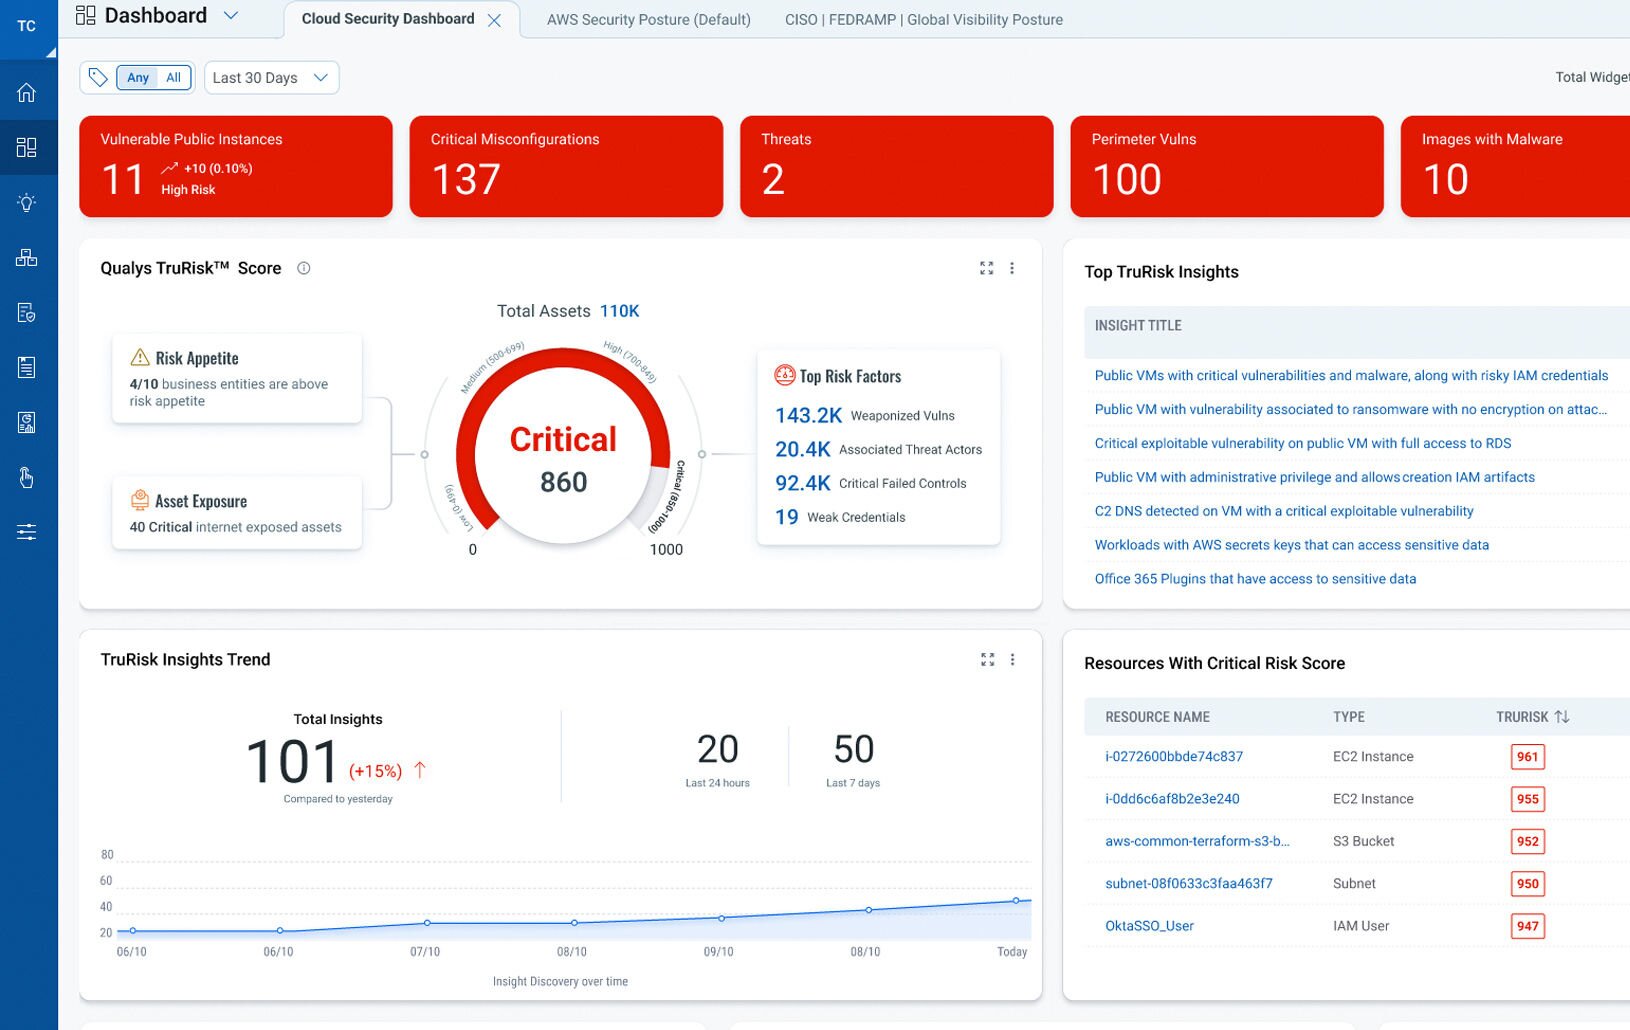
TotalCloud's TruRisk™ engine correlates vulnerabilities, misconfigurations, entitlements, and threat intelligence into a single, business-contextual risk score. Attack path analysis and blast radius mapping show how a single issue could cascade through your environment, helping CloudSecOps and CISOs quantify and communicate risk with clarity.
Instead of hundreds of alerts, you see the few that matter most, and can remediate them instantly via QFlow™ workflows integrated with ServiceNow or Jira. It's how TotalCloud transforms raw data into actionable insight and risk reduction.
Introducing TotalCloud™ with TruRisk Insights
FlexScan™ Multi-Mode Scanning
Combine agentless, agent-based, API, or snapshot scanning for comprehensive coverage of containers, VMs, and serverless workloads without performance or compliance trade-offs. FlexScan unifies findings under one risk view to eliminate blind spots.
Attack Path and Exploit Aware TruRisk-Based Prioritization
eBPF-Powered Runtime Protection
No-Code Remediation Playbooks With QFlow™
Audit-Ready Compliance and Reporting
Context-Driven Shift-Left Security

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Within just a few months of deploying Qualys Container Security, we designed an automated workflow to support our continuous integration and continuous delivery [CI/CD] pipeline in Jenkins. By automatically scanning our Docker images before deployment, we help our DevOps teams to ensure that they do not push vulnerable software into production.
Another thing that really impressed us about Qualys was the expertise, professionalism and dedication of their team. Throughout the implementation process and beyond, we have always been able to count on Qualys to give us the support and guidance we need.

Unlike vendors that surface raw CVEs, Qualys TruRisk™ connects vulnerability data with exploitability, threat intel, business context, and attack paths, surfacing the most impactful risks with clear, patch-ready guidance. This enables actionable, risk-aligned remediation across cloud, container, and application environments.

Through QFlow™, Qualys enables automated, contextual remediation using over 300 prebuilt workflows for patching, policy enforcement, and drift correction. Integrated with ServiceNow, Jira, and CI/CD pipelines, security, IT, and DevOps teams can orchestrate response in a unified, no-code framework.

Qualys FlexScan™ ensures complete, audit-ready visibility across cloud, on-prem, and container environments by combining agent, agentless, zero-touch network, and API-based scanning. This hybrid approach eliminates blind spots without sacrificing depth, speed, or coverage.

With out-of-the-box mappings for PCI DSS 4.0, HIPAA 2023, NIST 800-53, DORA, GDPR, and more, Qualys enables continuous compliance across global frameworks. Automated evidence collection and drift detection ensure audit readiness, without manual lift. FedRAMP High Authorization ensures full compliance with NIST 800-53.

Qualys uniquely correlates risk across code, APIs, workloads, containers, and SaaS, bringing together ASPM, SSPM, and AI-SPM for complete code-to-cloud visibility and remediation. From IaC misconfigurations to runtime threats, Qualys secures the full application lifecycle from Insecure dependencies To runtime applications.

With Qualys Units (QLUs), customers can mix, match, and reallocate licenses across any CNAPP module—CSPM, CWPP, CDR, KCS, SSPM, and more—without repurchasing or adding vendors. This delivers unmatched agility, operational simplicity, and cost efficiency at scale.
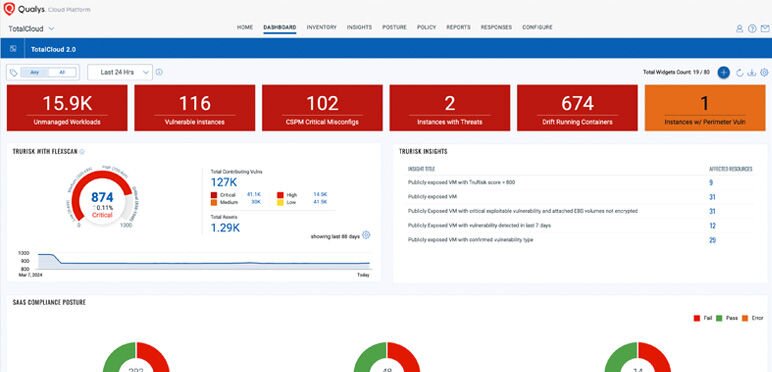
Drive data-driven decisions with actionable insights and customizable security dashboards.
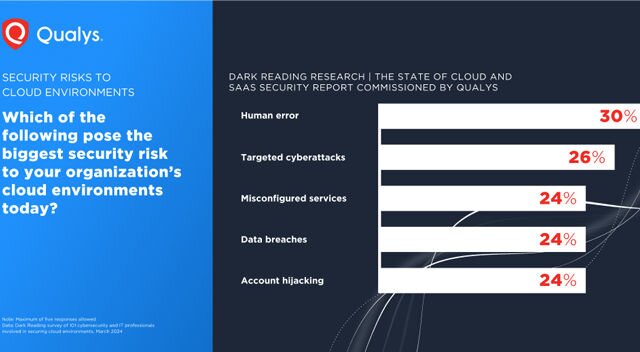
Cloud environments challenge IT security teams in prioritizing risk remediation. With evolving attack techniques, organizations need efficient tools and strategies to preemptively mitigate risks.
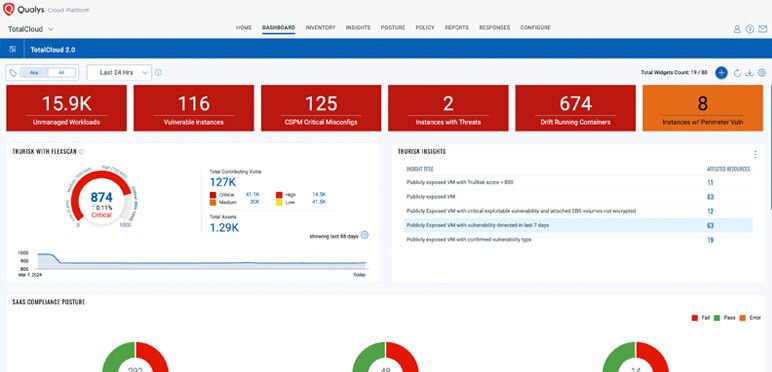
Discover risky assets and factors with actionable insights and customizable dashboards.
As attack techniques evolve, cloud environments face constant risk. Organizations need comprehensive solutions to learn trends and mitigate threats preemptively.
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.
Analyst Recognition and Related Resources
The Good, the Bad, and the Ugly of Cloud-Native Application Protection Platforms (CNAPPs)

A Cloud-Native Application Protection Platform (CNAPP) brings cloud posture, workload, identity, Kubernetes, development, and runtime security together so teams can understand and reduce risk across the full cloud application lifecycle. Qualys TotalCloud unifies these capabilities in one platform, correlating vulnerabilities, misconfigurations, identities, exposures, attack paths, and active threats so teams can focus on the risks that matter most.
Qualys TotalCloud supports major public cloud environments including Amazon Web Services (AWS), Microsoft Azure, Google Cloud Platform (GCP), and Oracle Cloud Infrastructure (OCI), with additional workload and Kubernetes security coverage for supported hybrid and on-premises environments.
TotalCloud uses TruRisk to enrich findings with factors such as severity, exploitability, exposure, asset context, threat intelligence, and business importance. Attack Path analysis then shows how multiple weaknesses can combine into exploitable routes, helping teams focus on remediation that meaningfully reduces risk.
TotalCloud correlates relationships among assets, vulnerabilities, configurations, identities, exposure, and other risk factors to visualize potential attack paths. This helps teams understand how an attacker could move from an exposed entry point toward high-value assets and identify the controls that can break the path.
TotalCloud connects predeployment security such as IaC and container scanning with deployed cloud posture, workload vulnerabilities, Kubernetes context, identities, and runtime threat evidence. This gives teams a continuous view from where risk is introduced to where it actually exists and matters in production.
Agentless methods provide fast deployment and broad coverage with minimal footprint, while agent-based approaches can provide deeper and more continuous workload visibility. Using both lets organizations balance coverage, depth, and operational overhead rather than forcing every workload into one model.
TotalCloud combines guided remediation with workflow automation through Qualys Flow and QFlows. Findings can be routed to the right owners, integrated with operational tools, and turned into repeatable remediation workflows to shorten the time between detection and risk reduction.
TotalCloud integrates with APIs, development pipelines, issue-management and ticketing systems, and security operations workflows so risk information can reach the team responsible for remediation. This helps cloud, development, and security teams collaborate without abandoning their existing operating processes.
TotalCloud provides asset and risk context that helps organizations route findings according to the type of issue and the team that owns the affected resource or workflow. Integrations and automation can then help send the finding into the appropriate remediation process.